Lost CAD Files: Why Your Firm Needs a Real Backup Plan
“We back up our files” is usually not a real plan, and one fire, theft, or ransomware hit can erase years of work.
Imagine showing up Monday morning, opening your project folder, and the files are gone. Not moved. Not renamed. Gone. Months of Revit models, AutoCAD drawings, and client work, just empty space where they used to be.
For a lot of small architecture and engineering firms, this is not a scary story. It already happened, or it is about to. One family firm we know well got hit by ransomware (a type of attack where criminals lock up all your files and demand money to unlock them). It took them down for three or four days. No drawings, no deadlines met, no work getting out the door, just panic.
The thing that saves you in that moment is not luck. It is a real backup plan. Not a copy on a thumb drive. Not “I think it syncs to the cloud.” A real, tested plan.
Here is the short version. A real backup plan keeps three copies of your files, on two different kinds of storage, with one copy kept off-site and out of reach of attackers. If a drive dies, a laptop is stolen, or ransomware hits, you can restore your work and keep going. That setup has a name, and we will get to it.
Prefer to watch? Here is the 9 minute video version.
“We back up our files” is usually not a plan
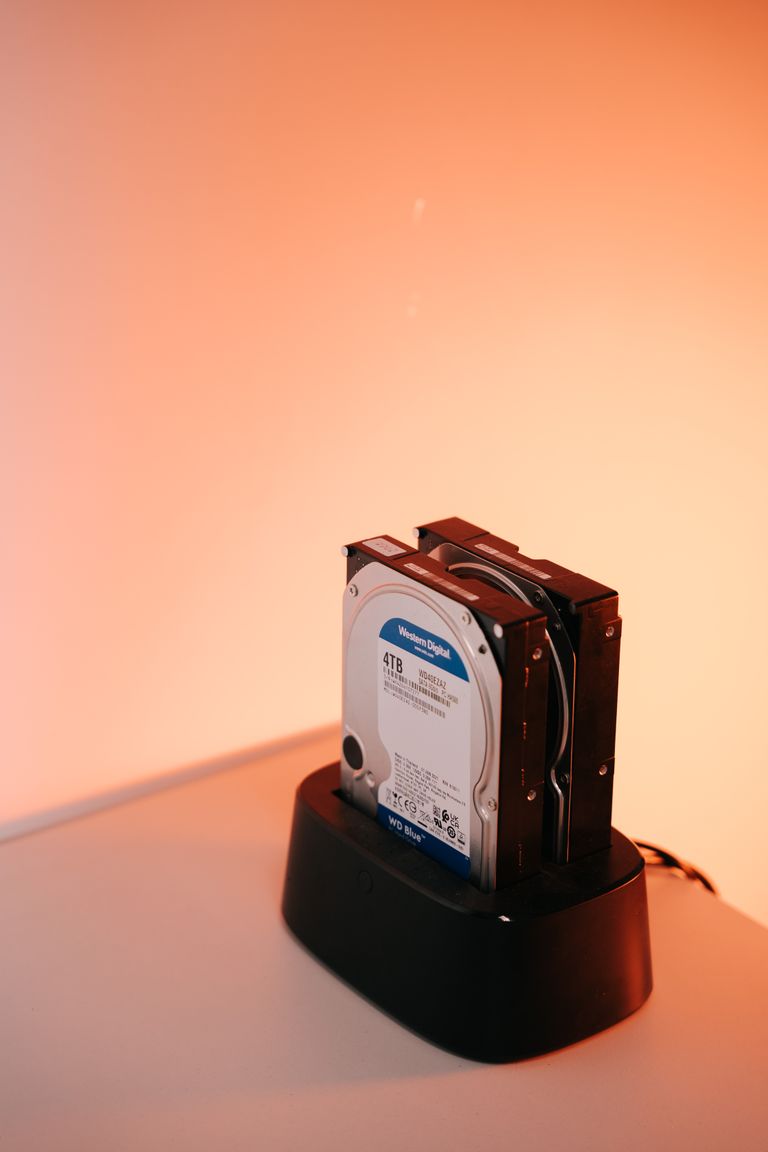
Many firms believe they are backed up, and they have something. Maybe an external drive someone plugs in now and then. Maybe files copied to OneDrive or Dropbox. Maybe a copy on the server.
Having something is better than nothing, and we are glad you are thinking about it at all. Most people are not. But let’s ask a few honest questions about that setup, because the gaps are usually bigger than people think.
- If your office floods or catches fire, is your backup in the same building? Then it burns too.
- If ransomware locks your server, does it also reach your backup drive that is plugged into that server? Usually, yes. The attack spreads to anything it can touch.
- If a file got deleted three weeks ago and nobody noticed, can you get the version from before it was deleted? Or did your “backup” already copy over the good version with the empty one?
- When did anyone last actually restore a file from the backup to make sure it works?
If those questions make you a little nervous, you are not alone. This is the gap between “we have a backup” and “we have a backup plan.”
One common gap deserves its own note. OneDrive, Dropbox, and SharePoint sync are not a backup by themselves. Sync copies every change everywhere, including deletions and files that ransomware has locked. The recycle bin and version history help, but they only go back so far. Your Microsoft 365 data needs its own backup too.
Three copies of your files, on two different kinds of storage, with one copy kept off-site and out of reach of attackers. That is the 3-2-1 backup.
What happens if you lose your files
Let’s be clear about the stakes, because this is not just an IT headache. For a design firm, your files are the business.
Your Revit models and CAD drawings are years of work. They hold your details, your standards, your client history. Lose them and you are not just redrawing one project. You are rebuilding everything. Some of it you cannot rebuild, because the client paid for it and the deadline already passed.
There is a money side too. If a project is late because your files are gone, you may miss a payment milestone. You may pay people to redo work the client already paid for once. And if you carry professional insurance (often called E&O, short for errors and omissions), a missed deadline from lost data is exactly the kind of mess that gets ugly.
What happens if you have a fire or a flood? What happens if an employee’s laptop gets stolen at the airport? What happens if someone clicks the wrong email link? A real backup plan answers all three the same way: you can restore and keep going.
Free download: Backup Restore Test Checklist
A simple checklist to prove your backups will actually restore your project files when you need them.
The rule that actually works: 3-2-1
Here is the plain-English version first, then the name.
Keep three copies of your files. The one you work on, plus two backups. Store them on two different kinds of storage, so one failure does not wipe out both. And keep one copy off-site, somewhere away from your office.
This is what the industry calls the 3-2-1 backup rule. It lines up with what CISA, the federal cybersecurity agency, tells businesses about ransomware: keep backups offline, encrypt them, and test them often.
For example, let’s say your live files sit on your office server. That is copy one. A backup runs to a separate device in the office, that is copy two on a different kind of storage. And a third copy goes to the cloud every night, that is your off-site copy. Now a single bad event cannot take all three. The fire that gets your server does not reach the cloud. The ransomware that locks your server does not automatically own your cloud backup. But if the cloud backup uses the same logins as your server, an attacker who steals them can reach it too. That is why the next piece matters.
Why ransomware changed the game
A few years ago, backups were mostly about hardware failing. A drive dies, you restore, done. That still happens. But the bigger threat now is ransomware, and ransomware is sneaky about backups.
Here is the trick the attackers use. They get into your network and they look for your backups first. If your backup drive is plugged into the server, they lock that too. Then when you go to restore, there is nothing to restore from. That is when firms feel forced to pay.
So the modern version of the rule adds one more piece: at least one backup copy should be immutable. That is a copy that is locked for a set time, so nobody can change or delete it during that window. Think of it like ink that cannot be erased until the lock runs out. How strong that lock is depends on how it is set up. Some setups still let an admin login shorten the lock, so have someone check the settings.
This is what we call an immutable backup. It is the difference between “we hope we can recover” and “we are confident we can recover.”
A backup you never test is not a backup
This is the part that gets skipped, so we will say it plainly. You should test your backups. A backup that has never been restored is just a guess.
Backups fail quietly. The job stops running and nobody notices, because backups are boring and nothing seems wrong. Until the day you need it. Then you find out the last good copy is from eight months ago, or the file is corrupt, or it was only backing up one folder the whole time.
Being proactive beats being reactive here, every single time. A good plan checks itself. Someone (or some system) confirms the backup ran, confirms the files are good, and does a real test restore on a schedule. We would rather find a broken backup on a quiet Tuesday than during a fire. Our 10 minute backup check shows you how to start.
What a real plan looks like for a small firm
You do not need an enterprise data center. Here is what a solid, right-sized plan looks like for a small design firm:
- Your working files on the server or workstations, like normal.
- A local backup to a separate device in the office, so day-to-day “oops I deleted it” recoveries are fast.
- An off-site cloud backup that runs automatically every night, so a fire, flood, or theft cannot take everything.
- At least one immutable copy, so ransomware cannot erase every backup you have.
- Monitoring and test restores, so you know it is working before you need it.
- Enough history that you can go back days or weeks, not just to last night, in case a problem went unnoticed for a while.
That is a real plan. Notice what it is not. It is not a single external drive on a shelf. It is not “it’s probably in OneDrive.” It is not something you set up once and never look at again. And if your server does more than hold files, see our post on what happens when your office server dies.
You are a small fish, and that is exactly why this matters
Small firms sometimes think they are too small to be a target. It does not work that way. Small firms often have weaker protection and no real backup, which makes them easier targets. You are the small fish in a big pond, and the big pond has sharks who count on you not being ready. We cover how they get in, in our post on ransomware.
The whole point of a backup plan is so you can keep doing the work you are good at, without one bad day erasing years of it. So you can focus on design, not disaster recovery.
Frequently asked questions
Let’s make sure you are actually covered
Our managed IT services help small architecture and engineering firms set up backups that follow the 3-2-1 rule, include an immutable copy, and get tested so you know they work. Based in East Tennessee. Serving firms nationwide. We take pride in the boring, reliable kind of protection that runs in the background and gets checked on a schedule.
If you are not sure whether your files are really safe, give us a call for a free IT checkup. We will look at what you have now, point out the gaps in plain language, and tell you honestly where you stand. No fear, no jargon.
Key takeaways
- “We back up our files” is usually not a real plan. A single external drive or “it probably syncs to the cloud” leaves big gaps, especially against fire, theft, and ransomware that reaches any backup plugged into your server.
- The rule that works is 3-2-1: three copies of your files, on two kinds of storage, with one copy kept off-site. Add at least one immutable copy (one locked so nobody can change or delete it for a set time) so ransomware cannot erase every backup.
- A backup you never test is just a guess. Monitor that the jobs run and do real test restores on a schedule, so you know you can recover before the day you actually need to.
Not sure your backups would survive a bad day?
We set up and test real backups (the 3-2-1 way) so a dead drive or ransomware never costs you a project. No obligation, no sales pitch.
Sources: #StopRansomware Guide (CISA); 2023 Ransomware Trends Report (Veeam)
3 Comments